Quick Takeaways
- An AI agent consent check reads permission live, not from snapshots.
- Re-read consent right before the write or the send.
- If the agent cannot read permission, the answer is no.
- Subscription status, email groups and consent fields all count.
- Log the permission the agent saw beside the action taken.
- Test with an unsubscribed contact before agents touch live records.
Table of Contents
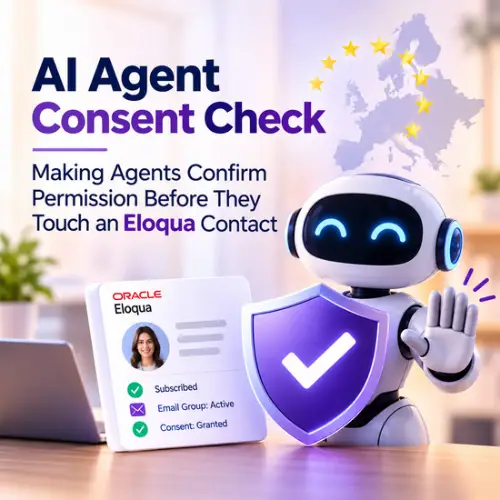
An AI agent consent check is the step that stops an agent from emailing someone who said no an hour ago. Your agent can update 3,000 contact records in the time it takes to refill your coffee, and if one of those contacts unsubscribed this morning, the segment it is working from may not know yet.
You have probably already governed the agent: what it can touch, who approves its work and what gets logged. But governance does not answer whether this contact, right now, still allows the action the agent is about to take.
This guide shows where permission actually lives in your Eloqua instance, how to build the check into the agent’s workflow and what to do when consent changes mid-task.
This post is for educational purposes only and does not constitute legal advice.
What Is an AI Agent Consent Check?
An AI agent consent check is a step in the agent’s workflow that reads a contact’s current permission immediately before an action, then stops or reroutes the action when permission is missing.
It sits next to governance, not inside it. Governing AI agents that touch Eloqua customer data sets the agent’s limits: its access, its approval gates and its audit trail. The consent check protects each contact inside those limits.
Why a List-Time Check Is Not Enough
Consent changes between the moment a segment is built and the moment an agent uses it. Agents often work from an export, a cached segment or an earlier API response, so an opt-out that arrived after that snapshot is invisible to them unless they look again.
Why consent is permission for a purpose in the first place is covered in the three checks behind privacy-safe AI. This guide picks up at the moment of action.
Which Agent Actions Need One
Tier the actions before you build. A practical approach is to tier AI decisions by consequence and reversibility, then map each agent action to a tier.
- Read-only analysis on aggregated data: usually no per-contact check.
- Writing to a contact record: check first.
- Adding a contact to a segment or campaign: check first, because entry comes before a send.
- Triggering or scheduling a send: always check, with no exceptions.
Where Does Permission Live in Your Eloqua Instance?
Permission in Eloqua does not live in one field, so your agent must read every source that applies. Eloqua’s native AI today is assistant-level, which means the agents your team builds reach your instance from outside through Eloqua’s first-party REST API. See where agentic AI in Eloqua stands today, and confirm what is live on your own instance before you design the check.
Subscription Status on the Contact Record
Eloqua subscription status is exposed on the contact record itself. Oracle’s REST API reference for the contact object lists isSubscribed, which shows whether or not the contact is subscribed, and isBounceback, which shows whether the contact has any associated bouncebacks. An isSmsSubscribed field also exists if your agent ever touches SMS.
Have the agent read these fields fresh at the moment of action. A value copied into a spreadsheet yesterday is not a consent check.
Email Group Subscriptions
A contact can be subscribed overall and still opted out of the email group your agent is about to use. Oracle’s guide to email groups explains that groups let you offer customized unsubscribe options instead of simply defaulting to the global unsubscribe list.
So the agent must check the email group that matches its action. How to read a contact’s email group status depends on your setup, so confirm the method with your admin or developer.
Your Own Consent Fields
If your team maintains its own consent and permission fields in your Eloqua segments, the agent must read those fields too, because subscription status alone does not tell it whether consent has expired.
How Do You Build an AI Agent Consent Check Into the Agent’s Workflow?
Build an AI agent consent check as its own step between authentication and action, decide in advance what a no means and record the answer with the action. Agentic AI consent comes down to one habit: the agent asks before it acts, every time.
Check at the Last Responsible Moment
A typical agent action follows four steps: request, authenticate, act and return, as described in how an agentic action flows through Eloqua’s REST API. Add a fifth step, check consent, between authenticate and act.
That makes it a real-time permission check, not a list filter. The agent re-reads the contact’s status right before the write or send, so an opt-out that landed an hour ago still wins.
Decide What “No” Means Before the Agent Runs
Agree the response to a failed check before the first run, not during an incident:
- Skip and log: the agent drops that contact, records why and continues with the rest.
- Hold the batch: the agent pauses the job when failures spike.
- Route to a person: the agent flags edge cases for review.
Fail closed. If the API errors, times out or returns an empty value, the agent treats the answer as no. Write that rule into the AI use policy for your marketing team.
Treat the Strictest Signal as Binding
When sources disagree, the agent follows the most restrictive one. An unsubscribe, an email group opt-out, a bounceback or an expired consent field each stops the action on its own, whatever the other fields say.
This is a design rule for your agent, not a description of how Eloqua resolves conflicts. It keeps the logic to a consent check Eloqua admins can read, test and explain.
Record the Permission the Agent Saw
Log the permission values the agent read, their source and the time, next to the action it took. If a contact asks why they were emailed, you can show what the agent saw.
Audit trail design itself belongs to agent governance, covered in the governance guide above.
What Happens When Consent Changes Mid-Task?
Withdrawals must win, even during a job that is already running.
Re-Check Long-Running and Batch Jobs
For a job that runs for hours, check each contact just before its own action, or at minimum at the start of every batch. Smaller batches keep data fresher but use more API calls, so agree sizes with your developer.
Withdrawals Must Win
For contacts covered by UK GDPR, the ICO’s guidance on valid consent says that when someone withdraws consent, you must stop processing based on it “as soon as possible in the circumstances.”
Build the agent so a withdrawal recorded mid-job applies to the next contact it touches. The risk is not only regulatory: one email to someone who just opted out can undo years of trust.
Test the Check Before the Agent Touches Live Records
Before go-live, create test contacts that should fail: unsubscribed, opted out of the relevant email group, bounced back and expired consent, plus an API error case. Confirm the agent stops on every one. The consent check Eloqua teams most often skip is the email group case, so test it explicitly.
Fold this into the oversight phase of running an AI agent pilot in Eloqua and repeat it whenever the job changes. A passed test is your evidence that the AI agent consent check works, not just that it exists.
Can One Permission Source Answer Every Agent?
Reading several sources per contact works, but every new agent repeats the same logic. One authoritative permission source makes the check simpler and more consistent.
4Comply records when and how consent is collected, verifies in real time whether permission exists for a given communication and keeps immutable audit trails of privacy activities. It integrates natively with Oracle Eloqua and Adobe Marketo Engage and offers a secure REST API. That means the agent workflows your team builds can be designed to ask 4Comply the same permission question your campaigns already rely on, instead of each agent stitching fields together on its own.
Conclusion
Governing your AI agents sets their limits, and an AI agent consent check protects each contact inside those limits. Without it, an agent can act on consent withdrawn an hour ago and still pass every governance review. Read permission live from every source that applies, fail closed when the answer is unclear, test the check with contacts that should fail and log what the agent saw. If you want help designing that check for your instance or connecting it to 4Comply, contact us.
About 4Thought Marketing
We're a B2B marketing automation and AI consultancy with a thing for getting complex tech to actually work. Since 2008, we've helped hundreds of organizations across financial services, technology, manufacturing, and real estate get more from Eloqua, Marketo, and their CRM integrations. We serve our clients across marketing automation strategy, lead lifecycle, AI, compliance, preference management, and more. Explore our services or get in touch.
Frequently Asked Questions
What is an AI agent consent check?
An AI agent consent check is a step in an agent’s workflow that reads a contact’s current permission right before the agent writes to the record, adds it to a segment or triggers a send. If permission is missing or unclear, the action stops or goes to a person.
Where does Eloqua store a contact’s subscription status?
Oracle’s REST API reference shows subscription fields on the contact record, including isSubscribed and isBounceback. Email group subscriptions and your own consent fields are separate sources, so confirm how each is configured on your instance.
Is an email group opt-out the same as unsubscribing from everything?
No. Email groups let contacts opt out of specific types of email. A contact can be subscribed overall and opted out of one group, so an agent must check the group that matches its action.
What should an AI agent do if it cannot read a contact’s consent?
Treat the answer as no. If the API errors, times out or returns an empty value, the agent should skip that contact and log why, or pause and alert a person.
How is a consent check different from AI agent governance?
Governance defines what an agent may do in general: access, approvals and audit trail. A consent check decides whether a specific contact allows a specific action at that moment. A well-governed agent can still act on stale consent, so you need both.